In enterprise B2B SaaS, power users, agency contractors, and executive stakeholders rarely operate within a single isolated account. They belong to dozens of distinct workspaces across multiple corporate organizations, each with disparate billing tiers, custom roles, and fine-grained access policies. When application navigation fails to communicate tenant boundaries clearly, users inadvertently trigger destructive actions in production environments or share confidential data across organizational walls. Designing a bulletproof multi-tenant workspace UX is a foundational prerequisite for enterprise security and retention.
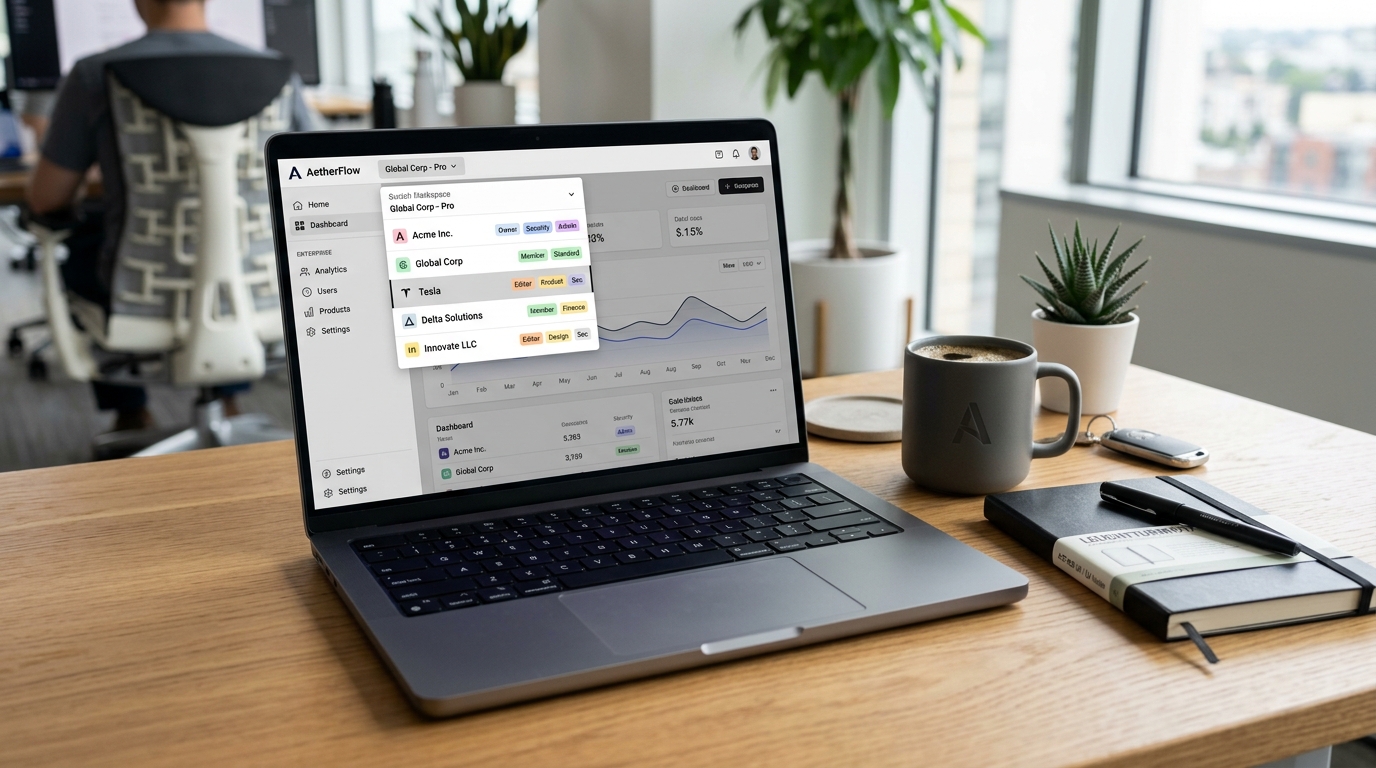
Multi-tenant B2B applications must enforce immediate contextual awareness at three distinct navigational levels: URL-level slug scoping (e.g., /app/:orgSlug/:workspaceId), an unmistakable header organization switcher with search and visual avatar disambiguation, and persistent full-viewport banner warnings during administrative or support impersonation sessions. Role-scoped action disabling must explain why a feature is disabled rather than silently hiding interface elements.
What Are the Core Requirements of Multi-Tenant Workspace UX?
The core requirements of multi-tenant workspace UX are: (1) URL-based tenant scoping ensuring state can be bookmarked and shared; (2) high-visibility organization and environment switchers featuring distinct color badges (e.g., Sandbox vs. Production); (3) persistent sticky alerts during user impersonation sessions; and (4) permission-aware interface controls that display contextual tooltips rather than vanishing completely.
When design teams build for single-tenant accounts, they rely on global session cookies. In multi-tenant environments, however, user identity is strictly separated from tenant tenancy. A single authenticated identity (e.g., `[email protected]`) possesses varying roles across organizations: they may be an Owner in Workspace A, a Read-Only Auditor in Workspace B, and a Suspended Member in Workspace C. The application shell must dynamically adjust its sidebar, route guards, and action buttons in real time as the active tenant context changes.
Organization Switcher Design Best Practices
The organization switcher is the primary control surface for tenant navigation. High-performing B2B interfaces implement four essential ergonomics:
| Design Dimension | Anti-Pattern (Friction / Risk) | Enterprise Best Practice |
|---|---|---|
| Tenant List Density | Unsearchable dropdowns that scroll off-screen | Virtualized list with instant filter search input and keyboard navigation |
| Environment Disambiguation | Identical styling across Dev, Staging, and Prod | High-contrast badge tags (Yellow = Staging, Red = Production) |
| Deep-Link Preservations | Switching orgs always dumps user to root dashboard | Preserves sub-route if valid in target org (e.g., /settings/billing) |
| Role Transparency | Hidden permissions; buttons mysteriously vanish | Disabled buttons with tooltips: “Requires Admin Role to modify” |
For related access control patterns, review our technical breakdown of ReBAC & Zanzibar UI Architecture in 2026 and B2B SaaS Reverse Trial UX Architecture (2026).
Support Impersonation & Audit Trail UX
Customer support and solutions engineering teams frequently utilize “Login As User” impersonation tooling to troubleshoot enterprise account anomalies. If poorly designed, impersonation creates catastrophic legal liability:
- Persistent Full-Width Notification Bar: A bold, fixed banner (e.g., amber or crimson) must render across the absolute top of the viewport stating: “You are currently impersonating [User Name] in [Tenant Name]. All actions are logged.”
- Prominent “Stop Impersonating” Button: The exit trigger must remain visible regardless of scroll position or sub-route navigation.
- Disabled Financial & API Secret Actions: While impersonating, destructive billing changes and raw API secret reveals must be hard-disabled in the client and verified server-side.
Multi-tenant navigation is the security frontline of enterprise SaaS. If a user cannot determine which workspace they are working in within 500 milliseconds of glancing at the screen, your interface architecture has failed. Invest in URL-scoped routing, persistent environment badging, and informative disabled permission states.
People Also Ask (PAA)
Why should multi-tenant URLs include organization slugs?
Including the organization slug in the URL (e.g., /acme-corp/projects) allows users to bookmark specific workspaces, share deep links, and open multiple tenants in separate browser tabs without session conflicts.
Should disabled features be hidden or greyed out in multi-tenant RBAC?
In B2B SaaS, disabled features should generally be visible but greyed out with an explanatory tooltip detailing the required permission or plan upgrade, rather than completely hidden, which causes user confusion.
What safety features must support impersonation have?
Impersonation requires a persistent high-contrast banner, an instant exit button, masking of sensitive payment methods, and immutable server-side audit logs for every user action.