RBAC UI Design: The Anatomy of Role-Based Access Control in B2B SaaS
Enterprise buyers evaluate security architecture long before their teams touch daily product features. When an IT administrator opens a workspace permissions tab, they expect clarity across three fundamental primitives:
- Principals: Users, automated service accounts, and API tokens.
- Roles: Bundles of permissions (e.g., Billing Admin, Editor, Read-Only Auditor).
- Scopes & Resources: Specific projects, workspaces, or database tables where roles apply.
For more foundational principles on enterprise architecture and monetization, check out our analysis on freemium-to-paid paywall UX playbooks and how design teams maintain consistency using multi-brand enterprise design tokens.
Enterprise Permission UI Comparison: 3 Structural Paradigms
| Architecture Pattern | Target Audience | Visual Complexity | Inheritance Clarity | Accidental Escalation Risk |
|---|---|---|---|---|
| Flat Role Selector (Owner / Member / Guest) | SMBs & Seed-Stage Apps | Very Low (Single Dropdown) | None (Explicit roles only) | Low, but lacks granularity |
| 2D Permission Matrix Table | Mid-Market & Scale-Ups | Medium (Resource vs Action grid) | Visual indicators for inherited rights | Moderate (Requires explicit save states) |
| Hierarchical Policy Builder (PBAC) | Fortune 500 Enterprise / Gov | High (JSON rules + Visual Logic) | Full lineage graph | High without strict simulation tools |
What Is an RBAC Matrix? Designing Enterprise Permission Grids in 2026
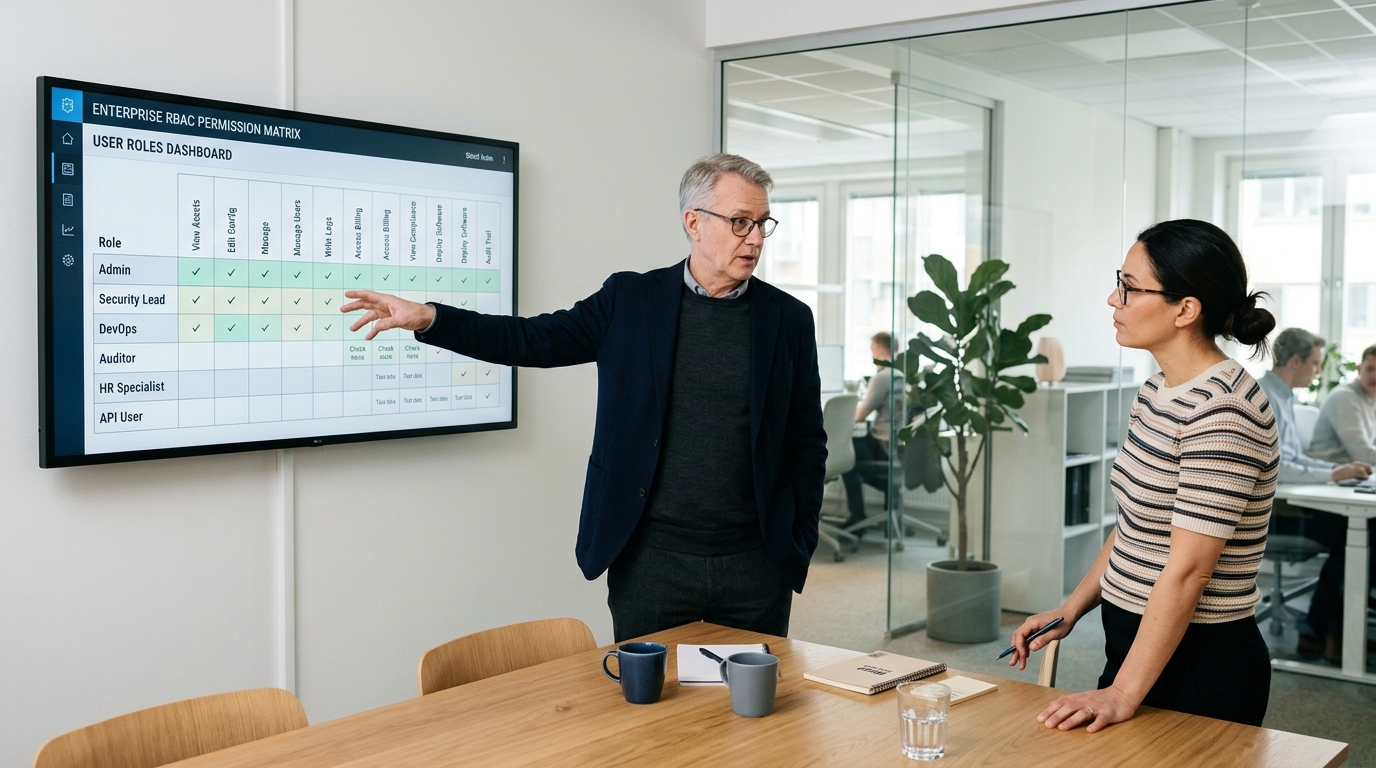
An RBAC matrix (Role-Based Access Control matrix) is a two-dimensional grid component in enterprise B2B SaaS that maps organizational roles along one axis against granular system resources and CRUD actions along the other. A permission matrix UI is a two-dimensional grid component in enterprise B2B SaaS that maps roles or users along one axis against system resources and CRUD actions along the other. It provides IT administrators with an instant visual audit of access rights, simplifies team-based role inheritance, and prevents accidental privilege escalations across complex workspace hierarchies.
RBAC UI Design Best Practices: 5 Rules for Enterprise Scale
1. Clear Visual Distinctions for Inherited Permissions
When an engineer is a member of the “Frontend Team” which already grants write access to Repository A, their individual user row must clearly show that permission as inherited (e.g., a muted lock icon with tooltip: “Inherited from @frontend-core”). Allowing admins to toggle individual checkboxes without explaining underlying team inheritance creates dangerous security assumptions.
2. Destructive Action Safeguards: The Double-Confirmation Modal
Revoking an administrative role or downgrading an owner’s access must never trigger from an accidental misclick. High-security interfaces implement contextual modal sheets that list all dependent systems, API webhooks, and active integrations that will immediately terminate upon role modification.
For more on structuring alerts without disrupting workflows, review our guide on toast notifications and snackbar anti-patterns.
3. “View As” Simulation Mode (The Fiduciary Sanity Check)
The gold standard of RBAC design is a sandbox preview mechanism. Before an IT administrator rolls out a new “External Auditor” custom role across 500 team members, providing an ephemeral “Preview UI as External Auditor” banner allows them to verify that confidential financial dashboards and API secret tabs are properly concealed.
4. Comprehensive Audit Trail & Diff Logs
Every permission change must generate an immutable, human-readable audit entry: “Rowan Croft altered ‘DevOps’ role: added secrets:read on Sept 7, 2026, 09:14 UTC”. Surfacing these diffs in the permission UI builds immediate confidence during enterprise procurement audits.
5. Micro-Typography & Scannable Scope Badges
Avoid sprawling walls of checkboxes. Group permissions logically under functional headings (Billing, Data Ingestion, User Management) and use compact, high-contrast semantic badges to represent read, write, and admin privileges. Explore our masterclass on micro-typography and visual hierarchy in SaaS dashboards for practical styling patterns.
Production UI: The Granular Scope Table Component
Below is a clean HTML/Tailwind mockup demonstrating an accessible, high-density RBAC permission matrix for modern SaaS applications:
Custom Role: Product Analyst
Read-only telemetry access across production and staging clusters.
| Resource Scope | Read | Write | Delete | Inheritance Source |
|---|---|---|---|---|
| Analytics Telemetry | ✓ | — | — | Direct Policy |
| Billing & Invoices | — | — | — | Explicitly Blocked |
| Feature Flags | ✓ | ✓ | — | Inherited (@engineering) |
Frequently Asked Questions: RBAC UI & Permission Matrix Design
What is a permission matrix UI?
A permission matrix UI is a structured grid component used in administrative interfaces to define and display access rights across system resources (such as billing, projects, or API keys) for specific user roles. It visualizes read, write, and delete permissions in an easy-to-audit tabular format.
How do you design an effective RBAC UI for B2B SaaS?
An effective RBAC UI requires clear separation between preset roles and custom scopes, distinct visual tags for inherited group permissions, simulation preview banners (“View As”), and strict double-confirmation safeguards for destructive privilege revocations.
What is the difference between RBAC and PBAC in UI design?
RBAC (Role-Based Access Control) assigns static bundles of permissions to predefined roles. PBAC (Policy-Based Access Control) evaluates contextual attributes (time, IP address, device security, resource tags) dynamically. PBAC interfaces require conditional logic builders, whereas RBAC relies primarily on two-dimensional permission matrices.
How should inherited permissions be displayed in a matrix table?
Inherited permissions should be styled with a muted or locked checkbox accompanied by a contextual badge indicating the parent source (e.g., “Inherited from @engineering-leads”). They should not be toggleable directly on the user level without modifying the parent group policy.
When scaling RBAC permissions into enterprise tiering, gating advanced role configurations requires seamless monetization UI. Review our teardown on: Contextual Paywall UX for B2B SaaS in 2026: Feature Gating Patterns, Inline Upgrade Triggers & Frictionless Conversion.
Related Compliance Design: To see how granular permission changes are tracked and audited for enterprise compliance, check out our masterclass on Enterprise Audit Log & Activity Timeline UX.