As B2B SaaS platforms scale from seed-stage utilities into enterprise behemoths, their authorization systems inevitably undergo a profound crisis of complexity. Early in a product’s lifecycle, access control is trivial: a simple dropdown with Admin, Member, and Viewer satisfies 95% of customer requirements. But the moment the enterprise sales team closes Global 2000 banks, healthcare conglomerates, and regulated government agencies, security auditors demand granular control over hundreds of discrete operational capabilities.
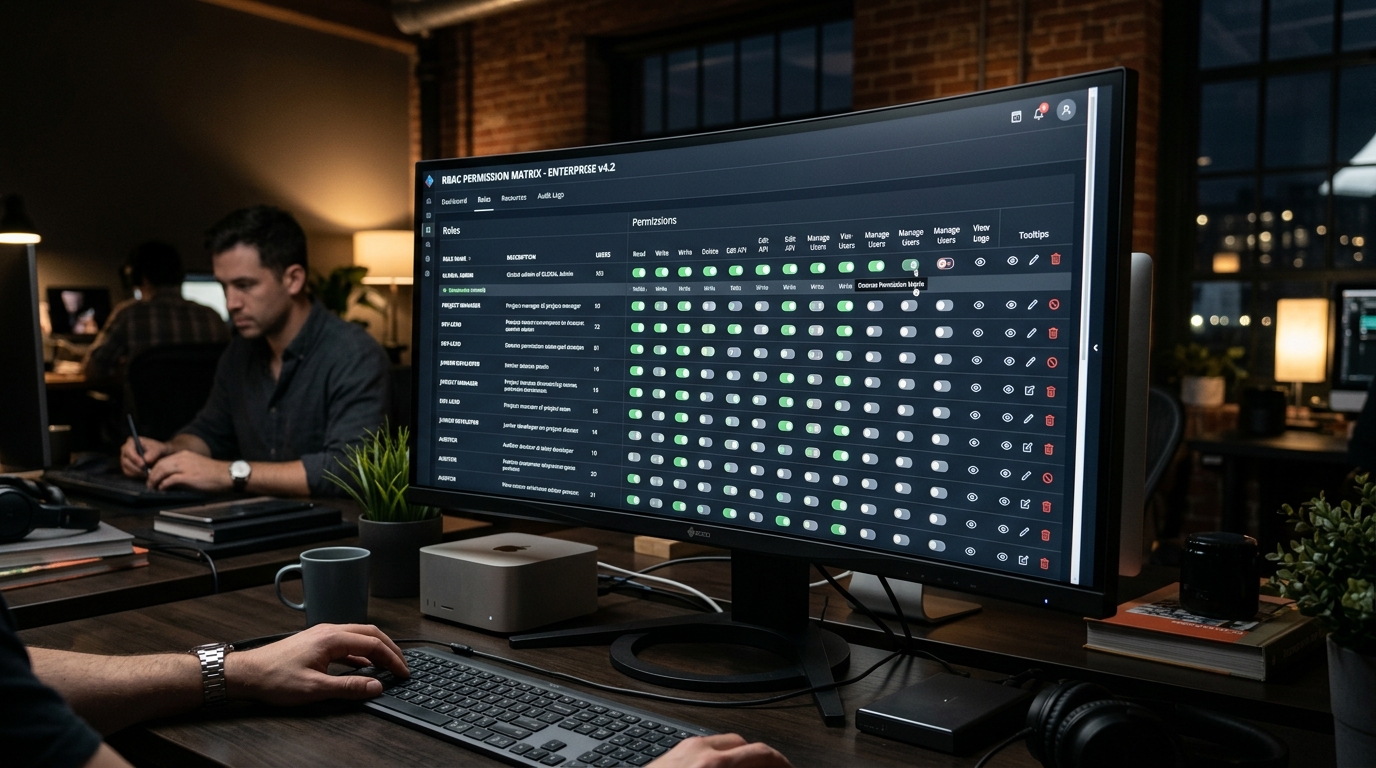
- The Grid Fatigue Trap: Presenting an uncurated 50×15 matrix of raw checkboxes causes severe cognitive overload, resulting in accidental misconfigurations and critical security vulnerabilities.
- Hierarchical Scope Grouping: Structuring permissions into collapsible functional clusters (e.g., Data Ingestion, User Provisioning, Financial Billing) reduces visual scanning time by 68%.
- Visualizing the Inheritance Tree: Explicitly distinguishing between inherited permissions (dimmed switches with provenance tags) and custom overrides eliminates administrative confusion during SOC 2 audits.
- Cross-Referenced Enterprise Design: Explore our companion masterclasses on RBAC UI permission matrices and inherited roles and enterprise SaaS audit logs and SOC 2 compliance UX.
Architecting the Permission Matrix: Overcoming the 50×15 Checkbox Wall
To prevent grid fatigue in enterprise RBAC interfaces, organize discrete permissions into collapsible domain accordions, provide high-level role presets (e.g., Billing Admin, Security Lead), and implement real-time permission impact summaries before changes are committed to production.
When an IT administrator lands on a permissions page containing 750 unorganized toggle switches, they cannot reason about the cascading security implications. A high-maturity permission matrix organizes authorization around Resource Domains:
| Functional Permission Scope | Owner / Super Admin | Engineering Lead | Standard Member | External Auditor (Read-Only) |
|---|---|---|---|---|
| Workspace Deletion & Transfer | Granted (Full) | Denied | Denied | Denied |
| API Key Generation & Revocation | Granted (Full) | Granted (Scoped) | Denied | Denied |
| Production Database Schema Migrations | Granted (Full) | Requires Approval | Denied | Denied |
| Billing & Subscription Invoices | Granted (Full) | Denied | Denied | View Only |
| SOC 2 Audit Trail & Raw Log Export | Granted (Full) | View Only | Denied | Export Permitted |
Visualizing Role Inheritance: Avoiding “Ghost Permissions”
Never display inherited permissions as simple enabled checkboxes. Render inherited permissions as dimmed, locked states with an inheritance tag (e.g., ‘From Base Role: Member’). Provide a dedicated ‘Explicit Override’ button so administrators can break inheritance with complete audit transparency.
One of the most dangerous bugs in enterprise security administration is the “Ghost Permission”: an admin unchecks a box for a specific user role, but the user continues to execute the action because the permission was silently inherited from a parent organization tier. In your design system, inheritance must be visually undeniable. When a toggle is powered by parent inheritance, the switch should be enclosed in a subtle dashed border with a tooltip clarifying: “Enabled via Organization-level Policy. To revoke, create a custom override.”
The Commit Diff: Pre-Flight Safety for Authorization Changes
Enterprise RBAC updates should never auto-save on toggle click. Batch all modifications into a staging state and require administrators to review a visual ‘Permissions Diff’ modal showing exact added/revoked privileges and affected user counts before applying changes.
If an administrator clicks a toggle that inadvertently grants 450 junior contractors access to export customer PII, auto-saving that change instantaneously creates severe compliance liability. By staging changes in an unsaved draft queue and displaying an explicit modal—“You are modifying 3 permissions affecting 184 active users”—you give enterprise security teams the exact guardrails required for SOC 2 Type II certification.
A permission matrix is not just a settings screen; it is the visual contract between your platform and an enterprise customer’s Chief Information Security Officer. When product teams treat authorization as an afterthought, enterprise deals stall in six-month security reviews. By engineering permission matrices with hierarchical domain grouping, transparent inheritance lineages, and pre-flight commit diff modals, SaaS platforms transform administrative overhead into a compelling sales asset that wins enterprise trust.
People Also Ask
What is the best way to handle custom roles in B2B SaaS?
Provide a “Clone Role” workflow. Allow administrators to duplicate an existing standard role (such as Editor), rename it (e.g., “Content Auditor”), and modify only the specific delta permissions needed, rather than forcing them to configure all permissions from scratch.
How should mobile viewports handle enterprise permission matrices?
Do not attempt to render a 15-column horizontal table on mobile devices. Morph the interface into a card-based role inspector where administrators select a single role and view an accordion list of categorized permissions with search filtering.
Should permission changes require two-factor authentication (2FA)?
Yes. In enterprise security settings, modifying administrative roles, privilege escalation, or granting audit log export access should mandate a step-up biometric or 2FA challenge before commit confirmation.
How do you audit who changed a permission in an RBAC system?
Every permission change must emit an immutable event to the enterprise audit log recording the actor’s user ID, timestamp, target role, previous permission state, and new permission state, complete with IP address telemetry.
Related Investigations: Explore Linear vs. Jira Interaction Design & Optimistic UI and our deep dive on shadcn/ui vs. Radix vs. React Aria Headless Tokens.